You probably haven’t looked lately, but if you did, you’d know that twitter[.]co is no longer owned by Twitter, er, X. The domain sat “for sale” for years before someone bought it sometime earlier this year. Now, it’s the first hop in a redirect chain: twitter[.]co > beaconhillpark[.]ca > postedecoute[.]ca, the last hop being a Cloudflare-fronted casino scam. (As if on cue with the latest on online casino scams, from Infoblox and our friend and advisor, Zach Edwards: https://www.infoblox.com/blog/threat-intelligence/how-money-laundering-scams-and-espionage-hide-in-a-web-full-of-casino-garbage/)
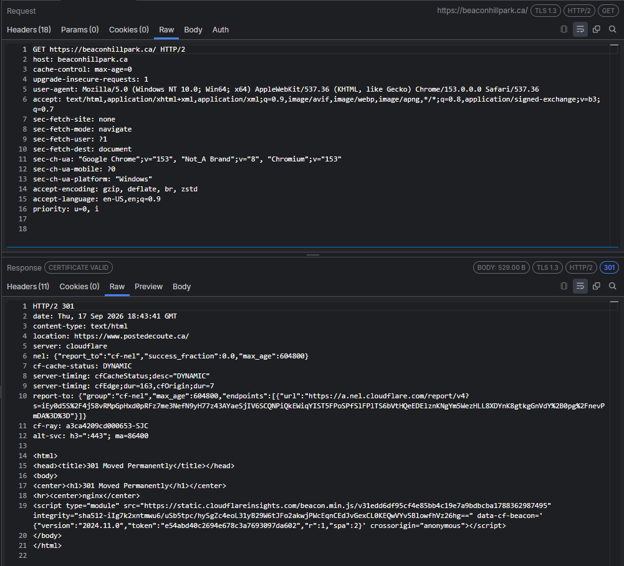 Figure 1: Twitter[.]co redirecting to beaconhillpark[.]ca
Figure 2: Beaconhillpark[.]ca redirecting to postedcoute[.]ca
All three domains trace back to the same WHOIS profile: a corporation name registered under an individual contact type and reused across every contact role.
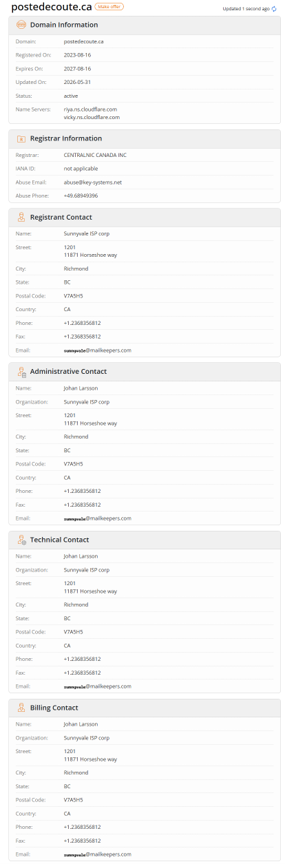 Figure 3: WHOIS for postedcoute[.]ca
This is typical of dropped-domain harvesting: grab a recognizable ex-brand name and funnel it into existing scam infrastructure.
And so, we leave you with the eternal reminder: make sure to keep your credit card info up to date for the domains you own.
RIP twitter[.]co, couldn’t have happened to a….ah, never mind.